Cybörü The autonomous hacker agent.
Cybörü is an autonomous AI agent that looks for zero-day (0-day) vulnerabilities on an authorised target: it maps, forms hypotheses, exploits and proves.
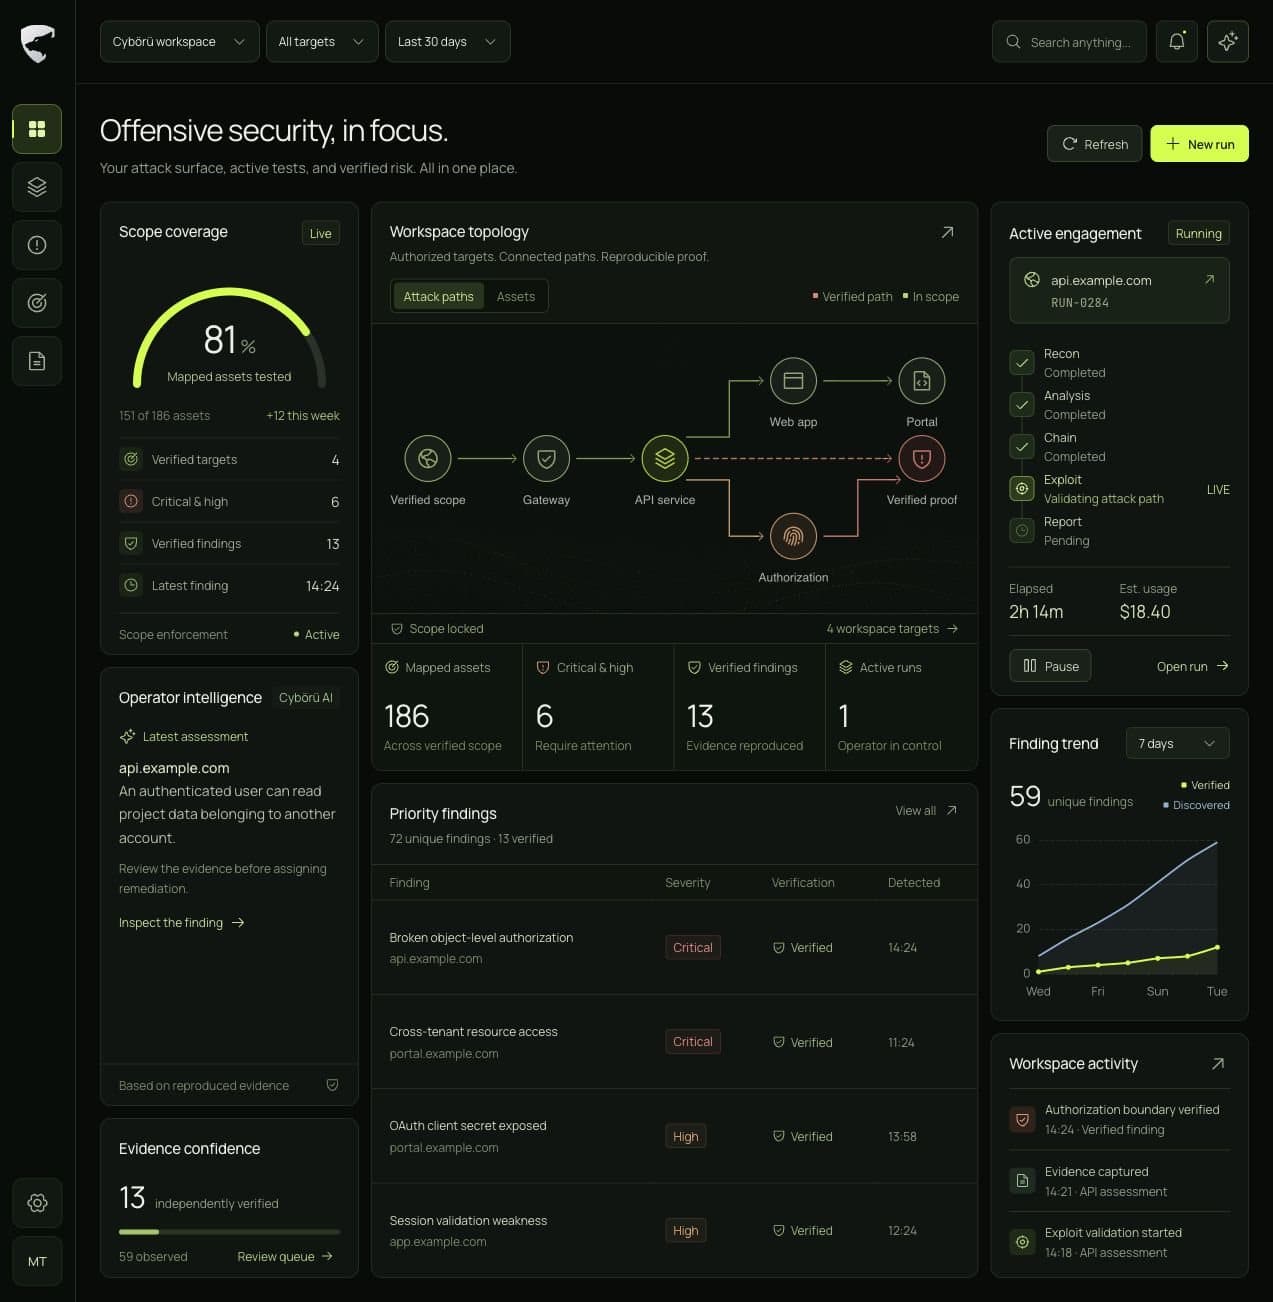
Product images are taken from the presentations in our promotional catalogue.
Who uses it
Used by cyber security, application security and technology teams. It gives a small security team the reach of a red team.
What problem it solves
Attackers who use AI do not stop, and traditional penetration testing cannot keep up. A penetration test is a snapshot: every release shipped between two audits goes live untested. Coverage is limited by the number of experts you can hire, so only a small part of the surface is tested. Scanners flag known patterns; they do not see the business-logic flaws an attacker chains into a breach. For a vulnerability, zero-day (0-day) is the day on which it is not yet known and has no fix. Cybörü is designed for this gap: it relies on reasoning about the target's own logic rather than on signatures or CVE lists, and it builds the multi-step attack chain automatically. No test can guarantee that it finds every vulnerability; that is why testing is repeated continuously.
Where Cybörü fits
Check every release
Run it before every deployment, so that new code ships tested rather than blind.
Cover the whole surface
Continuously test the assets a human team cannot reach in time.
Scale a small team
Give a small security team the reach of a full red team.
Demonstrate compliance
Continuous, evidence-backed testing for audits and KVKK obligations.
What Cybörü does
Scope is enforced on the network
Cybörü works only on authorised targets. Scope is enforced at the network layer, not in the model's instructions: private IP ranges, cloud metadata endpoints and every out-of-scope target are dropped on the network even if the agent is tricked.
- Egress is allowed only to targets on the allow-list; everything else is denied by default.
- Every run takes place in an isolated, single-use, ephemeral environment.
- The operator defines the scope and steers the run.
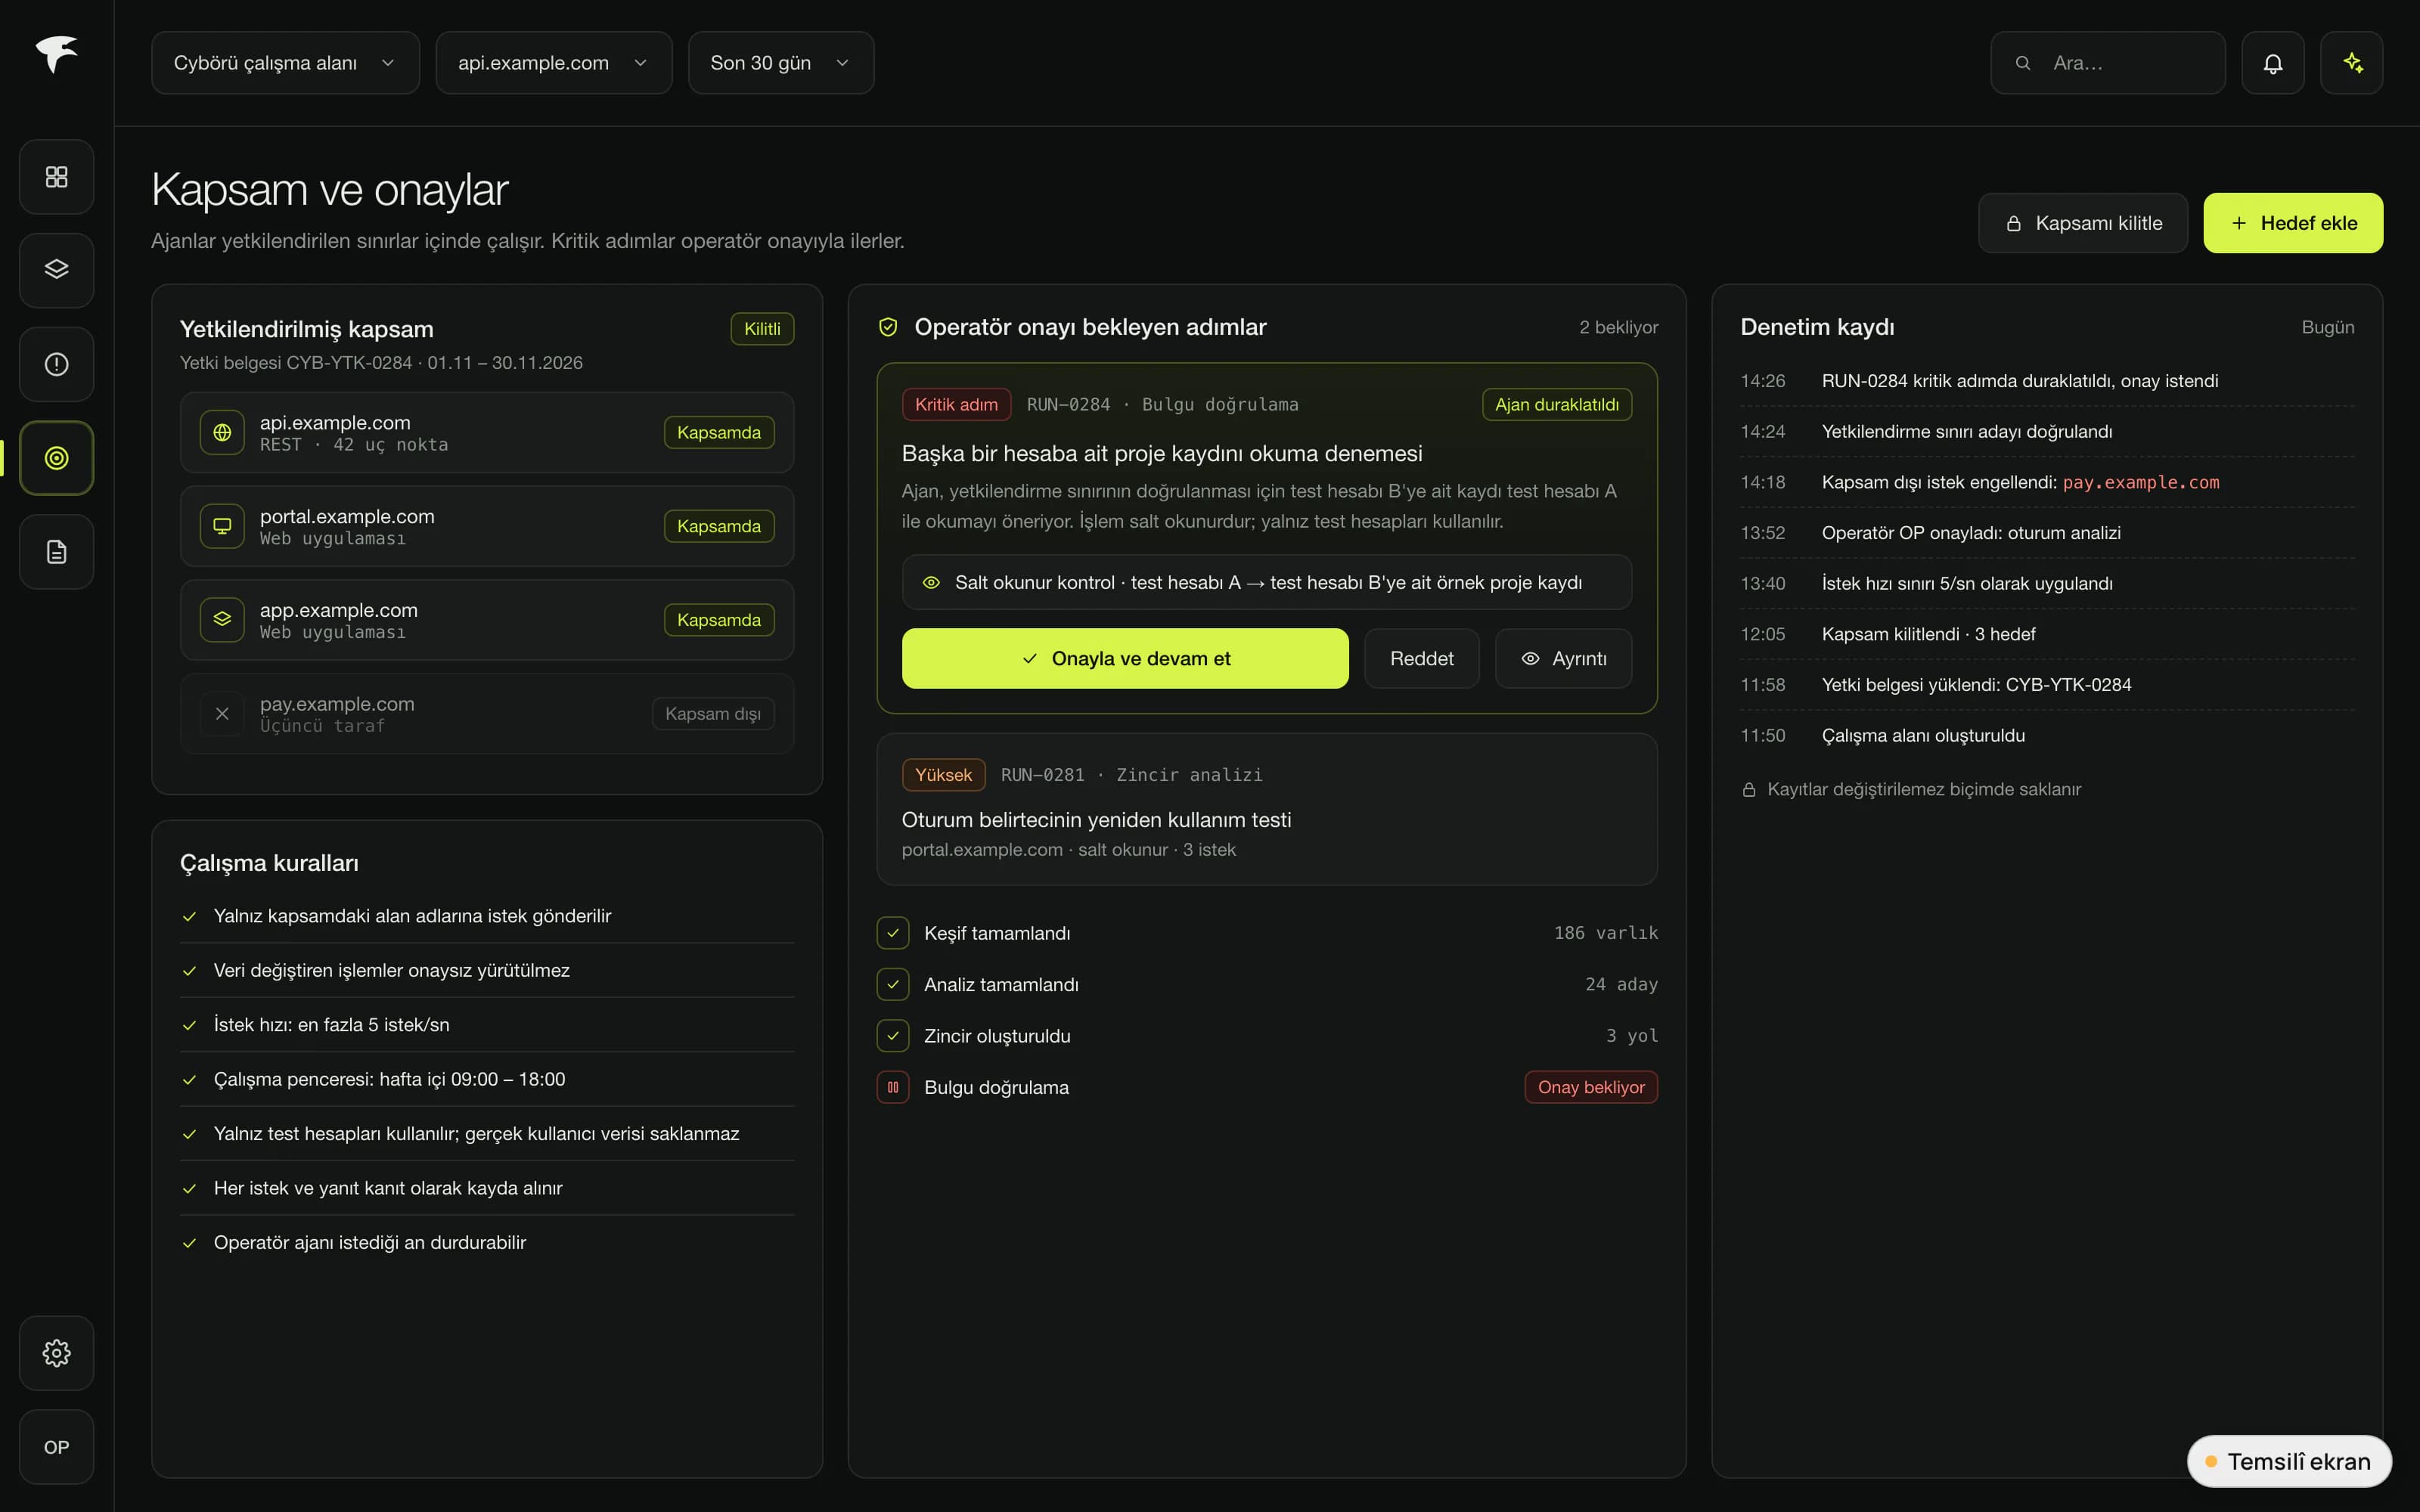
Illustrative screen Scope and approvals. Authorised targets, rules of engagement and a critical step awaiting operator approval. Proven findings
Every finding comes with a reproducible exploit path, a proof of concept (PoC) and remediation guidance. What is reported is not a theoretical score but the vulnerabilities an attacker can actually reach.
- Findings are de-duplicated and ordered by severity.
- The team can reproduce and verify the finding in its own environment.
- Reporting is in Turkish.
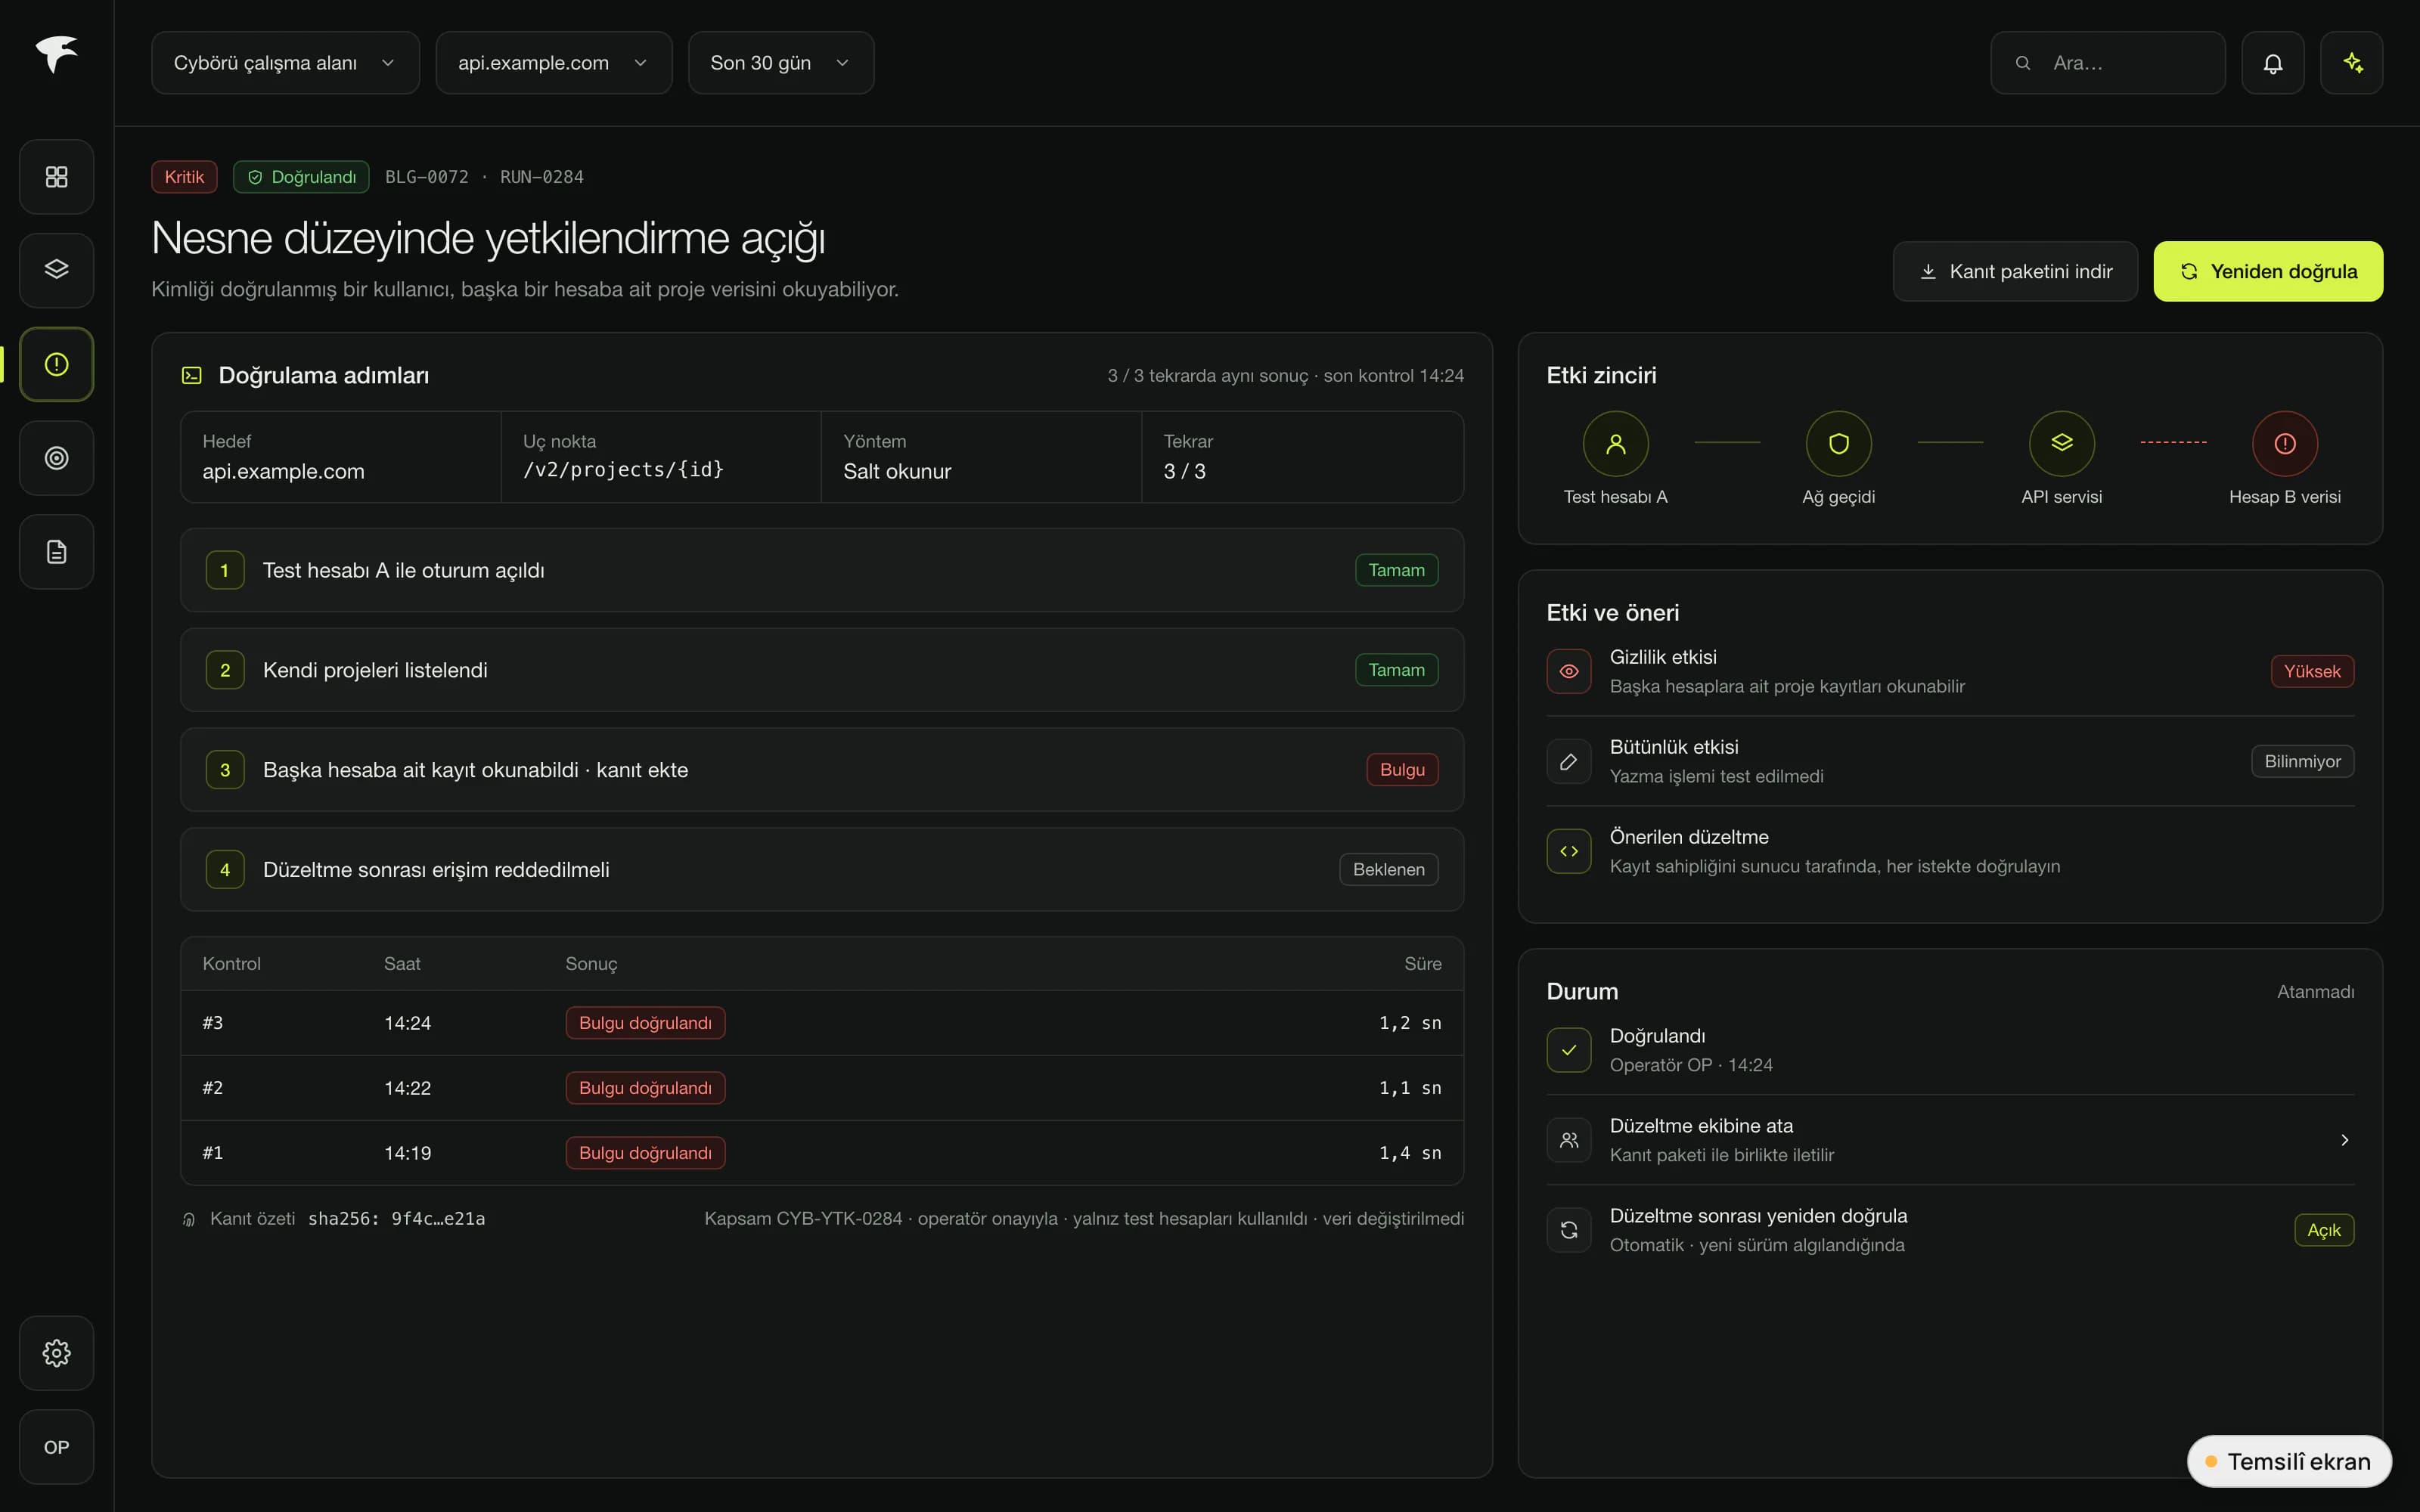
Illustrative screen Finding and evidence. Summary of verification steps, impact chain and recommended fix. Continuous testing
Penetration testing does not remain a one-off job. Cybörü runs before every deployment, so new code ships tested. Knowledge gained is kept from one run to the next.
- The surface opened by each new release is tested again.
- Assets a human team cannot reach in time are tested continuously.
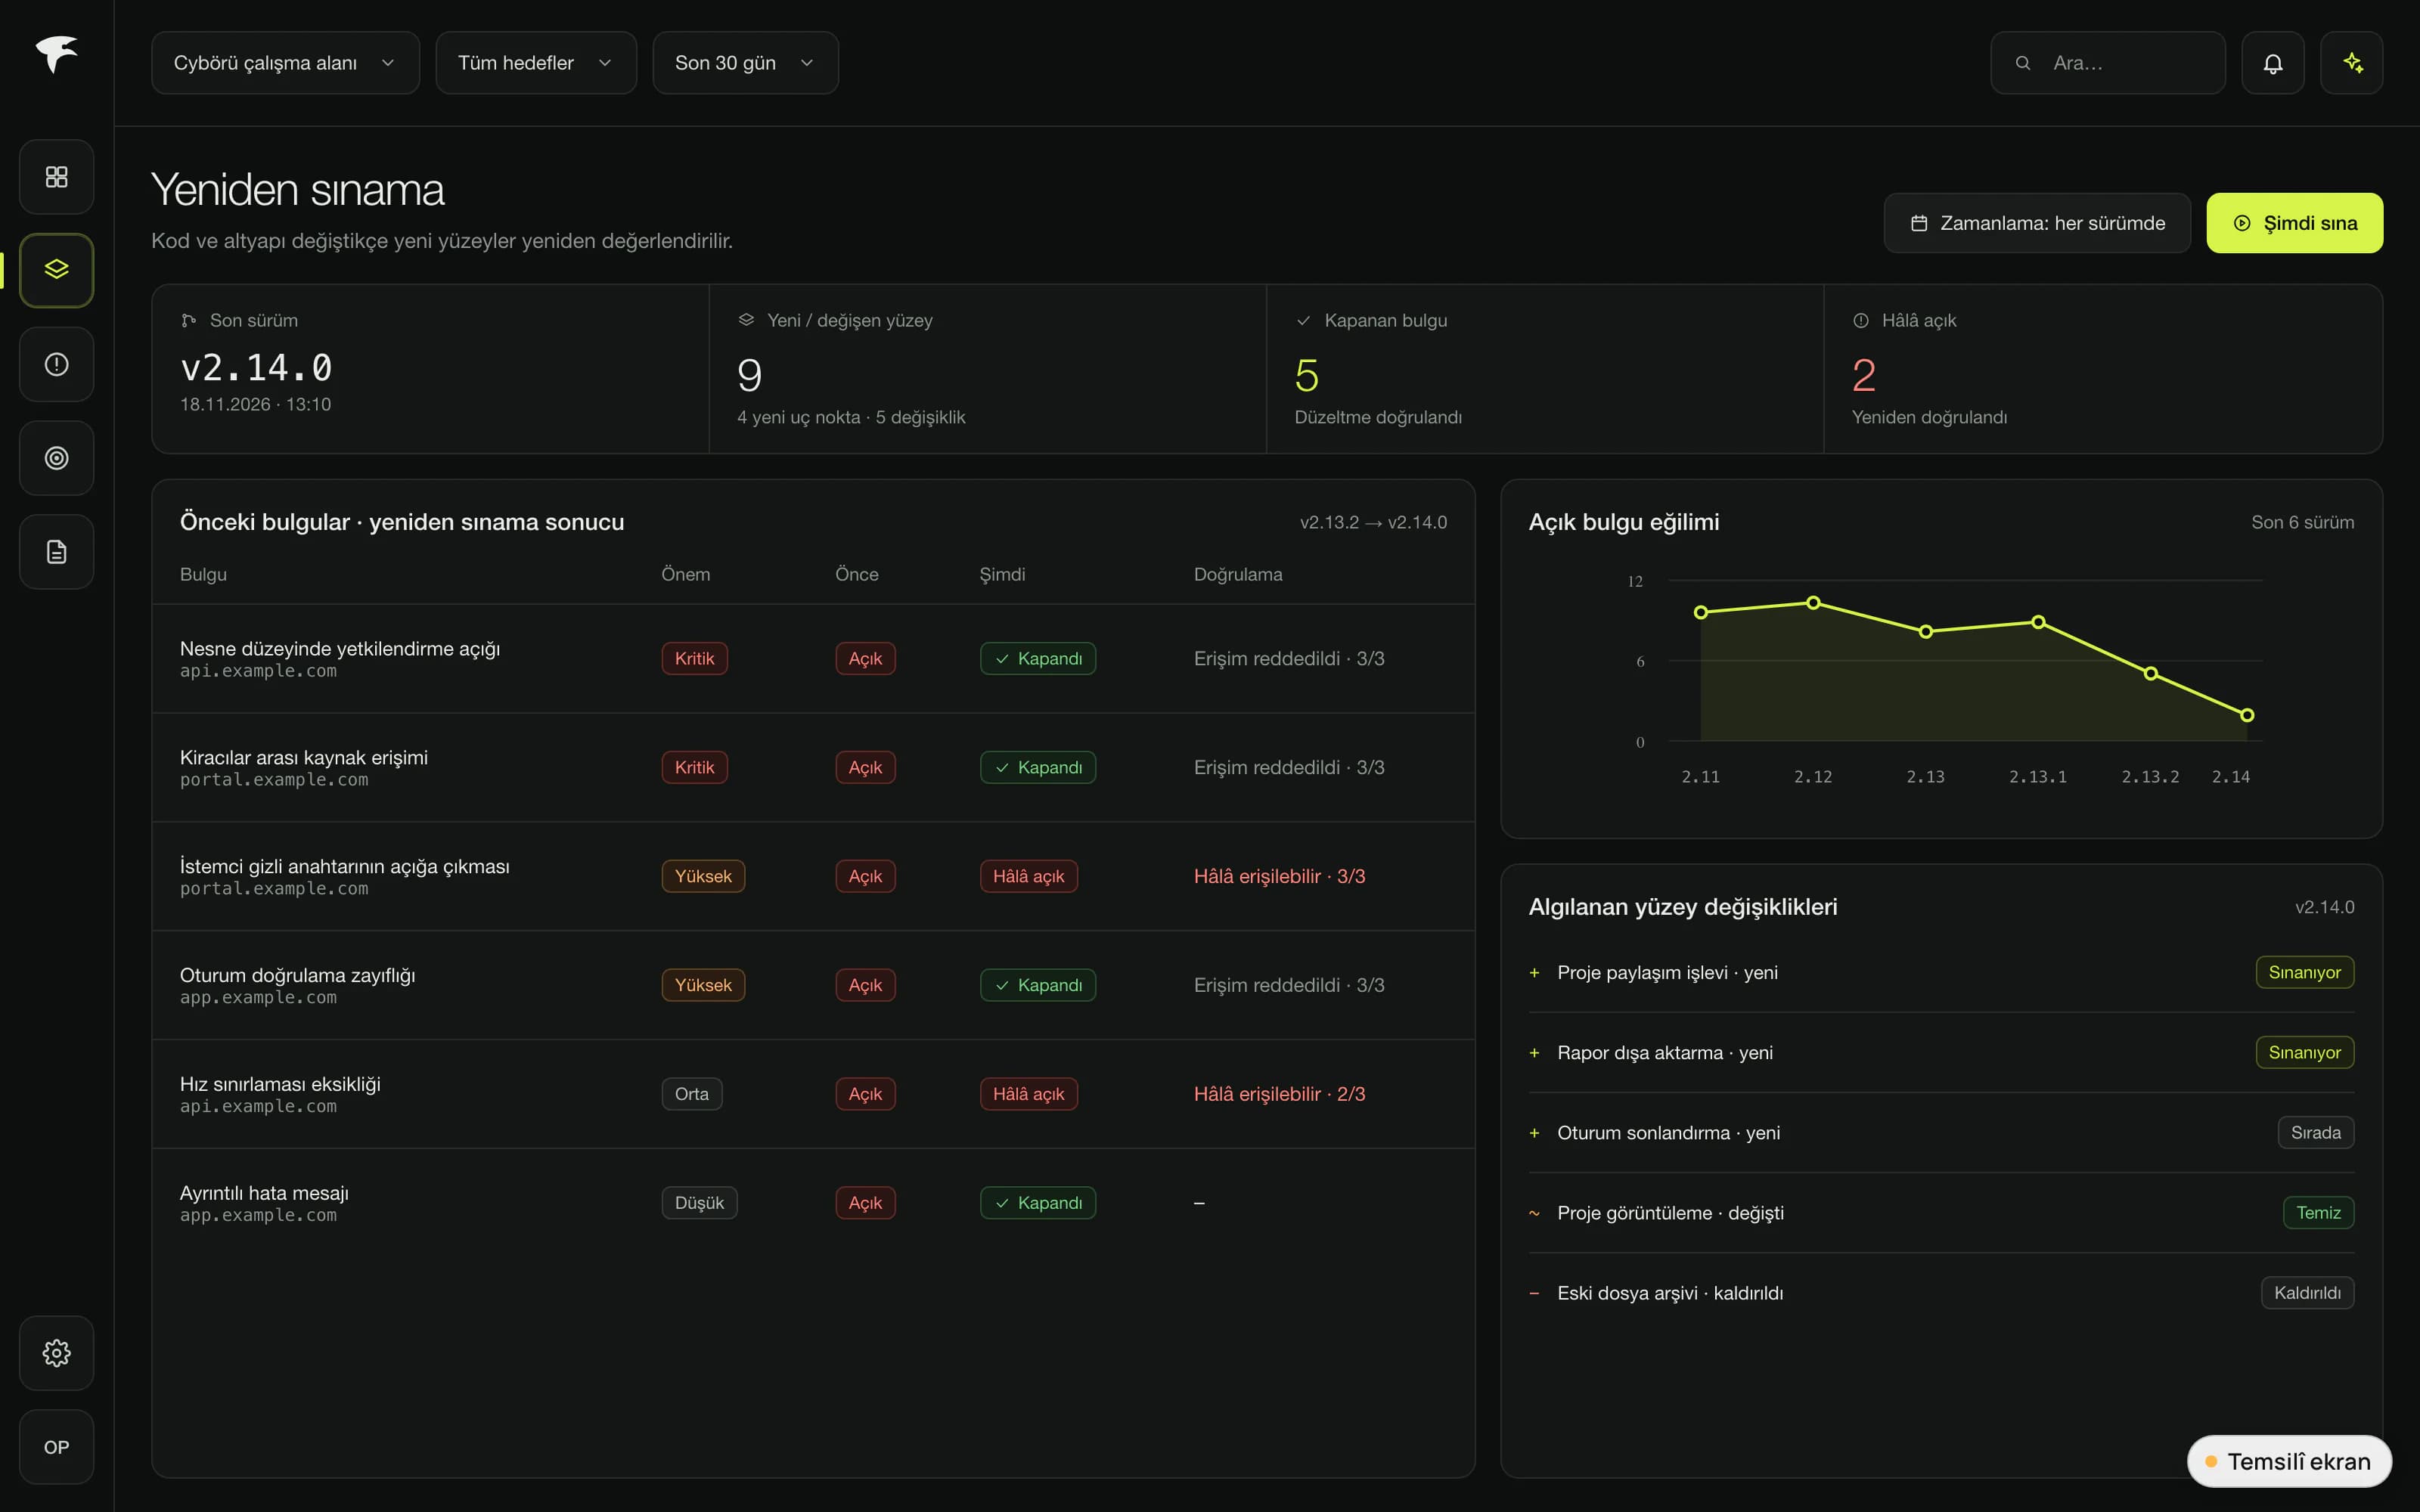
Illustrative screen Retesting. Status of previous findings in the new release and detected surface changes.
Autonomous discovery
The whole attack surface is mapped: servers, endpoints and exposed business logic. Overlooked risky areas become visible.
Multi-step attack chains
The agent models the trust boundaries of the intended behaviour and plans multi-step attack paths before it touches the target. By chaining steps it uncovers paths that shallow scanners cannot reach.
Business-logic flaws
It forms hypotheses about the application's own business logic and tests them with controlled experiments. It targets application-specific flaws that are on no signature list.
Local, with on-premises deployment
It offers reporting in Turkish, evidence handling aligned with the Turkish data protection law (KVKK) and the option to deploy on your own servers (on-prem); if you wish, your data never leaves your environment.
Strengthens the team
It frees your team from repetitive manual attempts; experts' time goes to reasoning and remediation.
Illustrative screens are prepared to explain what the product does; they contain no real institution, person or outcome data.
One continuous loop
- Discovery: the whole attack surface is mapped.
- Analysis: a trust-boundary threat model of the intended behaviour is built.
- Chain: multi-step attack paths are planned before the target is touched.
- Exploit: verified with controlled experiments, and the evidence is captured.
- Report: de-duplicated, evidence-backed findings are delivered and the loop starts again.
Frequently asked questions about Cybörü
Is Cybörü a vulnerability scanner?
No. Scanners look for known patterns. Cybörü is a reasoning agent that maps, forms hypotheses, exploits and proves; by chaining steps it looks for flaws in the application's own business logic.
Is it safe to point it at live (production) systems?
Cybörü is designed to run against production. Scope is enforced at the network layer: egress is allowed only to targets on the allow-list and everything else is dropped on the network. Every run takes place in an isolated, ephemeral environment.
Does it replace human experts?
No, it strengthens the team. The operator defines the scope and steers the run; Cybörü takes on the repetitive attempts, and experts' time goes to reasoning and remediation.
Can it be deployed on our own servers?
Yes. There is an on-premises deployment option; reporting is in Turkish.
Does it find every vulnerability?
No test can guarantee that it finds every vulnerability. That is why Cybörü runs continuously rather than once, and tests the surface opened by each new release again.
How does pricing work?
Cybörü is offered for a fixed annual fee, with no per-test charge. The price is not published on this page: the package and scope are set in a meeting.
Projects delivered with this product
Let's evaluate Cybörü together.
Let us test your security on a target of your choice. We define the scope and the authorisation together.
Let's talk